


For the last several months, I have been arguing that the boundaries between SIEM, AI SOC, security data infrastructure, and MDR are starting to collapse.
In March, I wrote that data pipelines had become the Trojan horse into the SIEM. In May, I argued that next-generation MDR had to become an AI-native SecOps control plane, not just a service wrapped around alerts.
The last two weeks have made those ideas look less theoretical. Vendors are now executing against them.
The Product Categories Are Converging
Microsoft announced ISOC in Defender, bringing SIEM and threat protection together around signals, context, agents, and response controls. This is more than another Copilot feature. Microsoft is trying to make the platform itself the integrated operating system for an agentic SOC.
Cribl launched Cribl Detect, moving directly from telemetry pipelines and data control into the SIEM market. This is exactly the progression I expected: first own the data path, then add search, detection, investigation, and response. Once a vendor controls how security data moves, it has a credible path toward owning more of the security brain.
Vega II combines a cyber-defense model, persistent memory, and access to data across lakes, object storage, SaaS tools, and legacy SIEMs. The important part is not the model alone. It is the harness around the model: context, memory, data access, human direction, and approval before consequential action.
Scanner is pushing federated indexing as an answer to the tradeoff between expensive SIEM ingestion and slow federated search. The idea is to leave raw data in its existing system of record while creating a compact index that can support fast investigation and continuous detection. Again, the direction is the same: cheaper access to more telemetry without forcing everything into one monolithic SIEM. I won’t go into the details of where federation won’t work, but it’s significant and this is not the solution to your storage problems.
TENEX is working with NVIDIA’s Open Agent Safety Platform to evaluate stronger runtime boundaries for security agents and to turn agent allow-and-deny activity into SOC evidence. That points to the next control layer. It is not enough for an agent to reach a conclusion. The system needs to govern what the agent is allowed to do, record what happened, and help operators understand why.
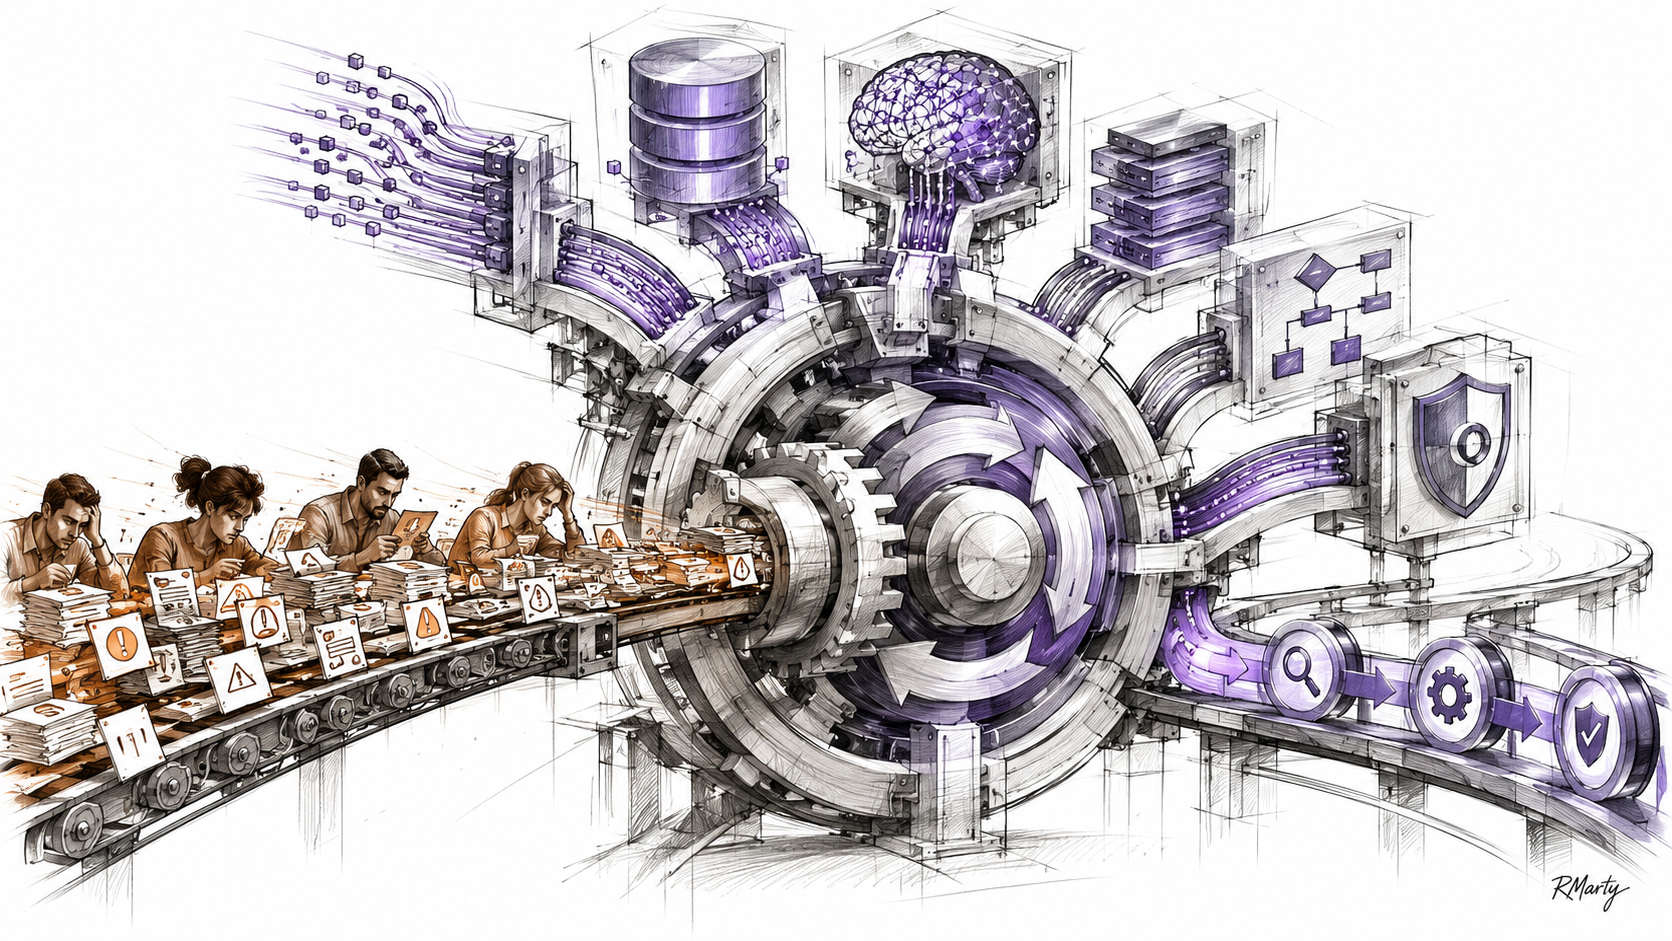
These are not five unrelated announcements. They are five versions of the same market movement. The new competitive surface is the full loop: data, context, detection, investigation, memory, policy, and action.
MDR Is Still Hard To Build And Hard To Value
The other important signal came from the services side. Quorum Cyber signed an agreement to acquire Ontinue, bringing together two Microsoft-focused security providers. Ontinue has more than 250 customers and had approximately doubled in scale under EQT, while building a strong story around an AI-powered MXDR platform. Financial terms were not disclosed.
My understanding is that the transaction valued Ontinue at roughly 2–2.5 times revenue. That is not necessarily a bad outcome, but it is also not a software multiple. It reflects how difficult MDR businesses can be to value.
MDR providers are normally valued more like managed services businesses, where EBITDA matters. The challenge is that many MDRs do not generate especially high EBITDA margins. Twenty-four-hour delivery, analyst staffing, customer-specific onboarding, detection tuning, incident escalation, and a growing number of exceptions all consume people. Recurring revenue helps, but revenue quality depends heavily on how much human effort is still required to deliver it.
This is where AI SOC capabilities and better operational software, products, and platforms become economically important. AI creates real value when investigations, customer context, detections, response policies, and operating knowledge become reusable product assets. If the platform lets the provider support more customers without proportional growth in analysts and exceptions, margins can expand and the valuation framework can begin to change. If not, the AI story is mostly positioning wrapped around the same services model. 80% margin is where the gold standard seems to calibrate.
The second opportunity is to expand what the customer is actually buying. I have argued in my previous MDR posts that the category has to move beyond alert triage and incident response into continuous risk reduction. That means helping customers understand what assets exist, where controls and telemetry are missing, which exposures matter, what should be remediated, whether the action happened, and whether risk actually went down.
That is not simply adding more services around MDR. It changes the role of the provider from outsourced alert handling to an operating control plane for security outcomes. It can increase wallet share, deepen the customer relationship, create more differentiated data and workflows, and make the platform harder to replace. More importantly, it gives the provider something more valuable to sell than analyst capacity. You’ll ask, isn’t that called an MSSP? Well, MDR’s might just have to deal with that.
Seen through that lens, a 2–2.5 times revenue outcome is an important market signal. The market is not going to award software-like value because an MDR provider uses AI or calls itself an agentic SOC. The provider has to prove two things: that its operating model gains real software leverage, and that its product can expand from processing alerts into reducing customer risk.
The Market Is Showing Us Where Value Will Accrue
The direction is becoming clearer.
Incumbents are pulling agentic workflows into integrated platforms. Data infrastructure vendors are moving upward into detection and SIEM. AI SOC startups are expanding downward into data access, memory, and control. MDR providers are consolidating and trying to turn delivery experience into product leverage and broader risk-reduction platforms.
The categories will keep their old names for a while, but the value is moving toward whoever can own the compounding control points: trusted data, operating context, detection quality, governed action, and the feedback loop that makes the system better after every investigation. And, again, a move to risk reduction and proactive security.
The market is no longer just talking about the agentic SOC. It is starting to build it.